DigitalXForce Blog
Start here if you are new to the blog
This is the DigitalXForce blog, for security, risk and compliance readers who want a plain answer to one question per article. If you are new, the four pages below define the ideas most articles build on.
What is TRiSCM
Trust, Risk, Security and Compliance Management, defined.
What is Continuous Control Assurance
How controls are validated on live evidence.
Third-party risk management
What it is and how it works.
DigitalXForce Glossary
Every platform term, defined once.
If an article matches a problem you have, request a demo.
Risk operations center vendors compared: DigitalXForce X-ROC, Qualys and Brinqa
September 29, 2026
No Comments

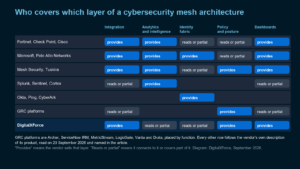
Cybersecurity Mesh Architecture Vendors Compared: Who Covers Which Layer
September 23, 2026
No Comments

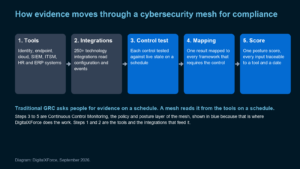
Cybersecurity Mesh Architecture for Compliance and Continuous Control Monitoring
September 23, 2026
No Comments

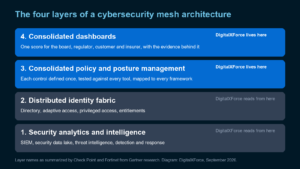
The Four Layers of a Cybersecurity Mesh Architecture, Explained for Risk Teams
September 23, 2026
No Comments


ServiceNow GRC and DigitalXForce: When Workflow Is Not the Same as Continuous Control Assurance
June 7, 2026
No Comments