
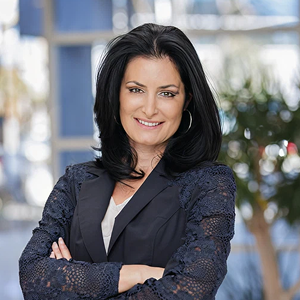
Margareta Petrovic

Margareta Petrovic is a senior cybersecurity executive with 15+ years setting strategy,
building global security programs, and architecting enterprise-scale solutions across
Fortune 500, public sector, and consulting environments. She serves as Chief AI Officer at
DigitalXForce, where she defines enterprise AI strategy and governance, chairs the AI
governance committee, and leads the convergence of AI and cybersecurity across the platform.
Prior to joining DigitalXForce, Margareta was Global Managing Partner for Risk and
Cybersecurity Consulting at Tata Consultancy Services, Global Head of Integrated
Cybersecurity Solutions at Wipro, and Health and Public Services Security Lead at Accenture,
where she delivered 50+ large-scale security programs for clients in heavily regulated
sectors. She has contributed to the World Economic Forum Cybersecurity Working Group, is a
member of the Forbes Business Council, and co-authored the TCS 2024 Cybersecurity Trends
report. Margareta holds CISSP and CISA certifications and is a Marquis Who's Who honoree.
Articles by Margareta Petrovic
Margareta Petrovic is Chief AI Officer at DigitalXForce, where she defines enterprise AI strategy and governance and chairs the AI governance committee. Her articles on this site explain how AI governance becomes a technical control and how Continuous Control Assurance (CCA) fits into Trust, Risk, Security and Compliance Management (TRiSCM).
- Monitoring Detects. Continuous Control Assurance (CCA) Validates.
- How Continuous Control Assurance (CCA) Fits Into Enterprise Trust, Risk, Security and Compliance Management (TRiSCM)
- Why Continuous AI Governance Requires Technical Controls
All articles by Margareta Petrovic
To see a control tested against your own stack, request a demo.


